The cloud security NIS2, DORA and the EU AI Act now demand, without the enterprise price tag.
Enterprise CNAPP suites cost six figures and a 20-person team. Telaris gives lean security teams across the EU & GCC one platform: cloud exposure, attack paths, intrusions caught in your own audit logs, and board-ready NIS2, DORA and EU AI Act reporting that emails itself to your stakeholders. Live in minutes, agentless and read-only.
30-day proof-of-value · no credit card · agentless, read-only · see how we compare
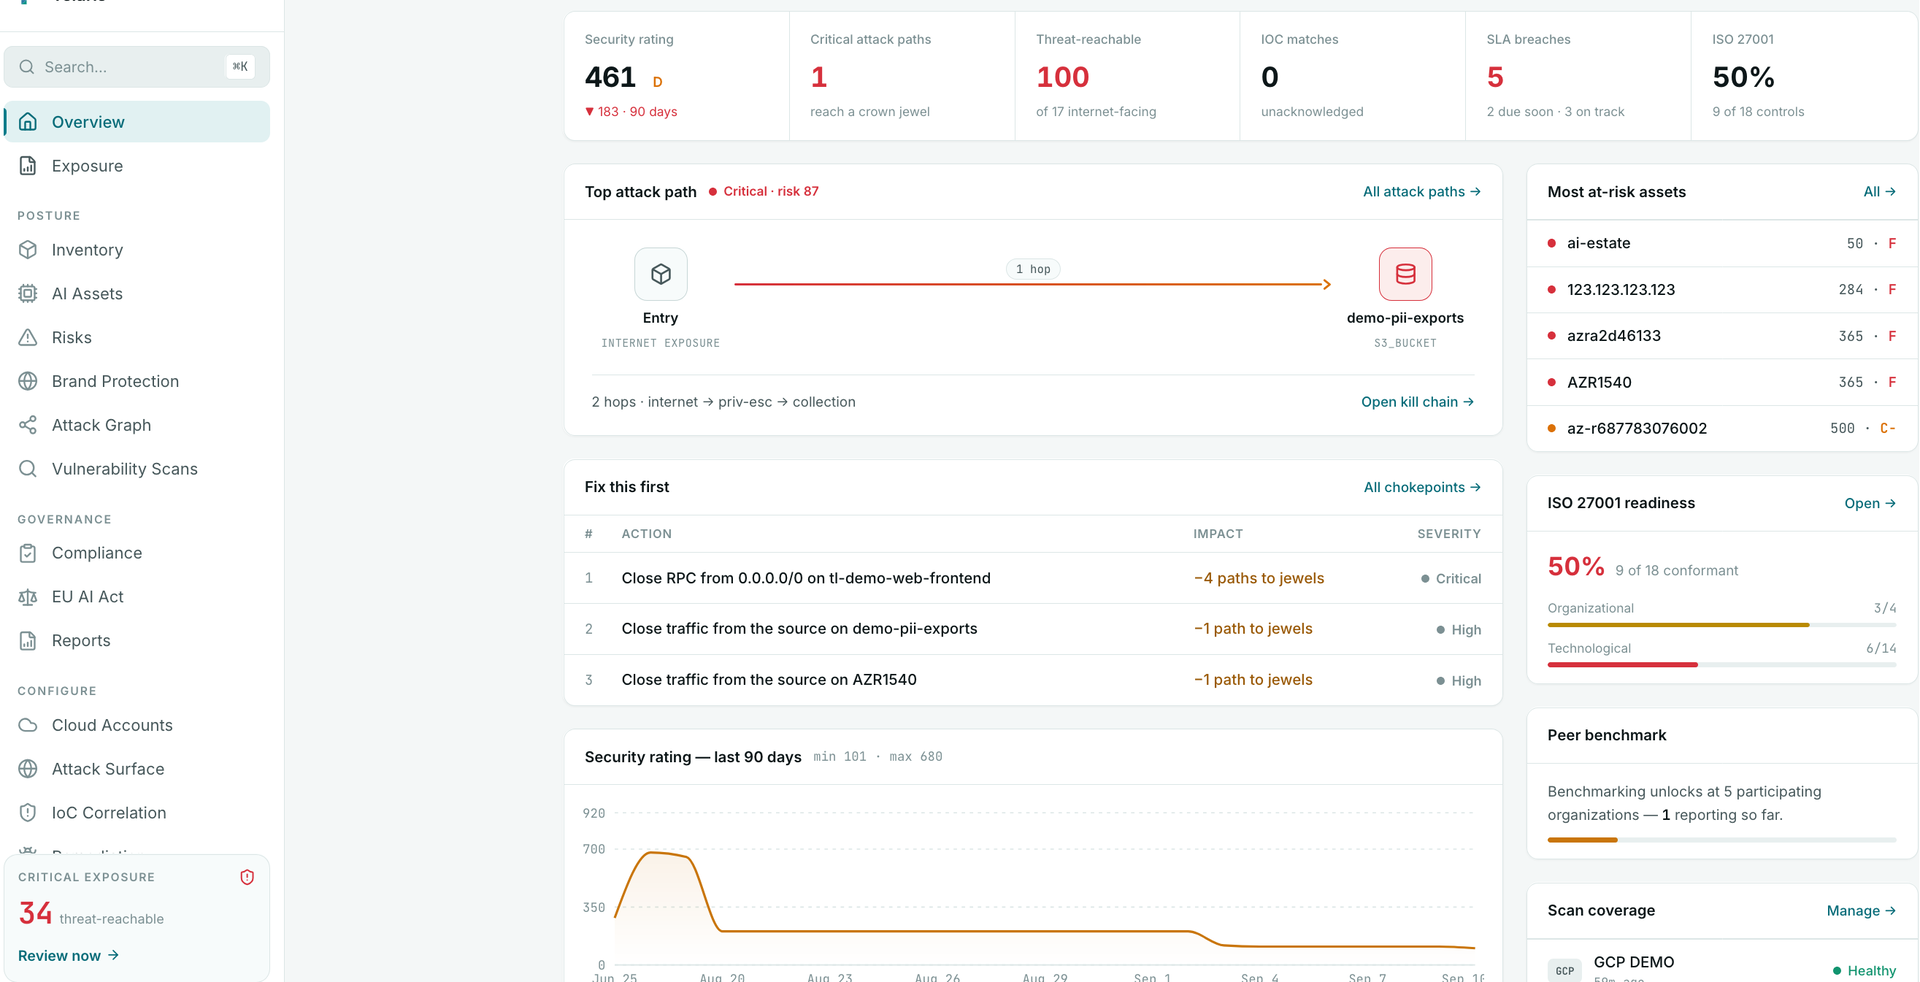
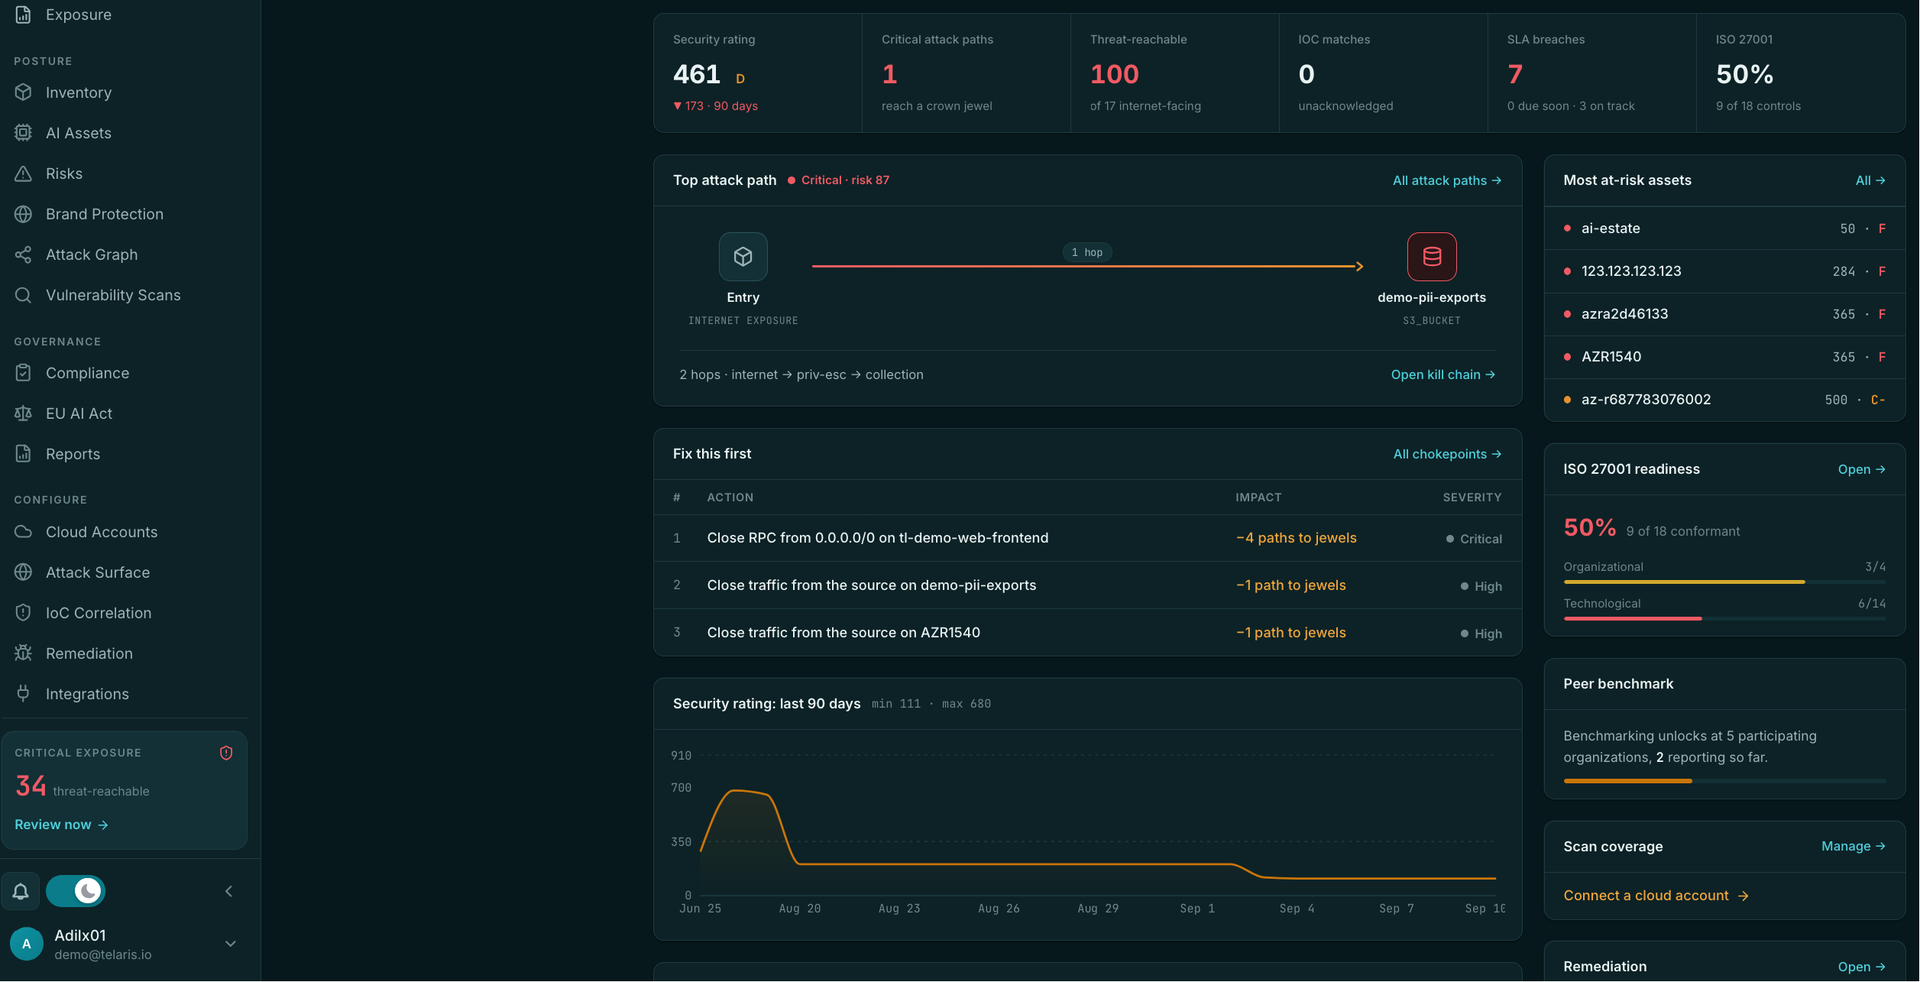
Engineered for regulated mid-market teams, EU & GCC
The five answers, before the sales pitch.
Everything a security lead needs to decide whether this is worth an hour. No form, no call.
- What does it cost?
- From €7,200 a year, published in full on the pricing page. No quote required to see it, and no per-seat charge.
- How long until it shows me something?
- Under 10 minutes from connecting a cloud account to a first scan. Nothing to install, so there is no rollout project in front of it.
- Where does my data live?
- EU infrastructure in Germany, which is where it stays. GCC-resident hosting is available on request.
- What access do you need?
- A read-only role you create in your own account. No write permissions are ever requested, no agent runs, and your cloud keys are never stored.
- What can I hand an auditor, or a board?
- 49 controls a scan can evidence across NIS2, DORA, the EU AI Act and ISO 27001, exported as dated PDF reports rather than screenshots. The audit section below sets out what is ready on your first scan and what only builds with time. A full sample is there too, with no form and no email required.
What this means for your risk review
- We can never change anything in your cloud. Read-only is the access model itself, not a permission someone could widen later. there is no code path that writes.
- Your keys are never stored. A role you create in your own account, revocable by you in one click, with no agent running anywhere.
- Your data stays in the EU, in Germany, and your logs never reach a language model, not for classification and not for enrichment.
- SOC 2 Type II and ISO 27001 are on the roadmap, not yet attested. You will hear that here before you have to ask for it.
The mid-market gap
Three bad options, and no fourth one.
Enterprise platforms
Too expensive
Enterprise CNAPP suites can run well into six or seven figures a year, take months to roll out, and need a sizeable security team to operate.
Six figures+ / yr
Open-source tools
Too fragmented
MISP and OpenVAS are free, but they mean 5–7 separate systems, dedicated DevSecOps expertise, and months of integration before anything works.
5–7 tools to stitch
Doing nothing
Too risky to ignore
The bill arrives long before the regulator does. Insurers want evidence at renewal and price the absence of it into your premium. Enterprise buyers send a security questionnaire before they sign. “We’ll get to it” costs a deal and a renewal first, and carries personal accountability for management when it finally costs a fine.
Premiums, lost deals, then fines
12,000+ mid-market companies (200–2,000 employees) across the EU and GCC have no integrated, affordable cloud-security solution. Telaris closes it.
Internet-originating attack path analysis
Nothing on this path is a critical finding on its own.
That is why a severity-ranked list never surfaces it. Each step is ordinary: a load balancer facing the internet, a metadata service left on, a role that can read a secret, a database doing its job. The route they form is not ordinary, and it ends at your customer data.
- Internet
0.0.0.0/0
internet
- Entry
alb · edge
public by design
- Foothold
ec2 · payments-api
IMDSv1 enabled
- Identity
secrets · app-role
instance role
- Data
rds · customers
PII
How it connects: SSRF reaches 169.254.169.254 and the instance role is handed over
Enforce IMDSv2, hop limit 1
One instance setting. The application keeps working; the credential hand-off stops.
The Capital One chain, 2019.
Every one of these is four or five findings a scanner would rank low, and one change that breaks the chain. Telaris ranks the chains, not the findings, and tells you which single fix closes the most of them.
See the paths in your own estateOne platform · twelve modules
Everything a security team needs, in a single pane.
No five-tool stack, no six-month rollout, twelve modules in one platform, running on your live cloud data, tied together by one risk model and a ⌘K jump-to-anything search.
Cloud Asset Discovery
Agentless inventory across AWS, Azure and GCP, scanning starts within minutes of onboarding. Every asset gets a single pane: its CVEs, threat matches, attack paths, endpoints and scan history in one view.
How it worksAttack Path Analysis
A graph engine that surfaces toxic IAM and network combinations before an attacker can use them, scored on how easy a path is to walk and how bad it is if someone does, with the chokepoints that close the most at once.
How it worksThreat Detection
Reads your cloud audit logs for the sequences that look like an intrusion rather than a Tuesday, grouped into one scored incident per identity. No log line reaches a language model, and a source we could not read is shown as unread, never as clean.
How it worksThreat Intel Feeds
Real-time IoC aggregation with an "Affects you" lens. Every article is matched against your actual CVEs, products and stack, so you read what targets you, not a global firehose.
How it worksCompliance Evidence
One-click NIS2, DORA, ISO 27001 and SOC 2 reports generated from live data: control-by-control conformance, an ICT asset register and the trend over time. It records evidence and never claims you are compliant.
How it worksEU AI Act Evidence
You cannot evidence AI you have not found. Agentless discovery surfaces the model endpoints, agents, vector stores and MCP servers already running in your cloud, then works out which duties attach to each, and when.
How it worksIncluded in every plan
Brand Protection & Typosquatting
Look-alike domains caught from certificate transparency and new-domain feeds, scored and triaged, with takedowns prepared for your approval and monitored afterwards.
Unified Risk Feed
CVEs, misconfigurations, threat-intel hits and brand impersonators in ONE prioritised feed, with real-time alerts to Slack, Teams or email.
Vulnerability Scanning
Continuous internet-facing scanning, ranked by exploitability instead of raw CVSS noise.
AI Security Analyst
A RAG-powered analyst grounded in YOUR estate, answering with your open CVEs and exposed assets in context, not generic advice.
IoC File Scanner
Upload a file, extract indicators and correlate them against your environment in seconds.
Executive Reporting & Trends
Board reports emailed on schedule, a weekly "what changed" digest that leads with wins, and trend lines for findings burn-down, attack surface and compliance drift.
Telaris vs. the field
Where we win, and where we don’t.
Wiz owns the attack-path graph. Tenable owns deep vulnerability scanning. We say so below, so that the rows where only one column is filled mean something.
| Capability | Telaris | Wiz | Orca | Tenable | MISP |
|---|---|---|---|---|---|
| Risk Score Timeline · posture trend over time | |||||
| Cloud asset discovery | |||||
| Brand / domain protection | |||||
| Attack path / graph | |||||
| Threat-intel feeds | |||||
| AI analyst grounded in YOUR estate | |||||
| IoC file scanner | |||||
| Vulnerability scanning | |||||
| Board reports · no-login PDF links | |||||
| EU residency & NIS2/DORA | |||||
| Entry plan under €10K / year |
Based on publicly available product information as of June 2026 and reflects our own assessment. Vendor capabilities change over time, names and trademarks belong to their respective owners.
Audit preparation
The audit date is set. The evidence is not.
Most of audit preparation is archaeology. Someone rebuilds the asset register in a spreadsheet, fills a folder with console screenshots, and writes the narrative from memory two weeks before the assessor arrives. Telaris exports the same evidence as a dated PDF generated from the live estate, and the first one is ready on the day you connect.
Ready on your first scan
Under ten minutes from granting a read-only role to a report you can send.
ICT asset register
DORA Art. 8 names this duty outright and NIS2 21.2.i assumes it. Generated from discovery on every scan instead of maintained by hand in a spreadsheet nobody trusts.
Conformance deviations
49 control entries across ISO 27001, SOC 2, NIS2 and DORA, each one printed with the finding that produced it so the assessor can follow the number back to its source.
Deviation appendix
The detail an assessor asks for once they have read the summary. Included in the auditor pack, dropped from the board version, because the two audiences want opposite things.
Attack paths and exposure
The routes through your estate, each one shown with the single change that closes it. This is the section that turns a findings list into a remediation plan.
Three sections that cannot be backdated
Posture trend, assessment cadence and incident handling are evidence of a programme managed over time, which is what ISO 27001 and NIS2 are actually asking for. They cover the period you have been scanning and no earlier. Connect six weeks before the assessment and you have six weeks of it, which is six weeks more than a scan run the week before. This is the one part of the pack that rewards starting early, and it is the reason to start now rather than in the next budget cycle.
Four packs, one scan behind them
Auditor evidence pack
Everything, mapped to ISO 27001 and SOC 2, with the deviation appendix.
NIS2 readiness
The modules that evidence Art. 21(2) measures, mapped to NIS2 and DORA.
Board summary
Posture, movement and the fix-first list. No appendix.
Customer trust report
What a prospect may see. Asset names redacted.
Telaris certifies nothing, and no report it generates says you are compliant. It produces the technical evidence an assessor asks for, with the scan date and the source of every number printed on the page. The determination stays with your auditor, which is where an assessor expects to find it.
No form. No email address.
Threat Detection · Cloud audit logs
When it happens, you will be asked when it started.
Your cloud already records every action every identity takes, and almost nobody reads it. Each line looks ordinary on its own: a login, a policy edit, a secret read. The sequence is what is not.
Three findings an analyst has to spot are related, or one incident that reads as a chain.
ci-deploy@prod
one identity · 32 minutes
- 1
Sign-in from an unusual pattern
09:14Initial Access
- 2
Role trust policy widened
09:31Privilege Escalation
- 3
Secret read for the first time
09:46Credential Access
- Rule severity
- +45
- 3 ATT&CK tactics
- +24
- Reached a crown jewel
- +20
Reads the log you have
CloudTrail, Azure Activity and GCP audit logs, read where they already land.
One incident per identity
Signals grouped per principal on a sliding window, and scored where you can see the sum.
Already in ATT&CK language
Every step carries its MITRE technique, so it arrives in your IR plan’s words.
Evidence for detect-and-respond
The named duty in NIS2, ISO 27001, SOC 2 and DORA, evidenced with real incidents.
Risk Score Timeline
A score without a timeline is just a grade.
Every competitor can tell you how exposed you are today. Telaris shows you where you stood 90 days ago, what changed, and why the number moved, recorded automatically on every scan, from the day you connect.
- Your board sees a direction, not a snapshotWalk in with evidence that risk fell for two quarters straight, instead of a list of open findings that only ever looks bad.
- Auditors get continuous improvement, evidencedISO 27001 and NIS2 both want proof that your posture is managed over time. The timeline is that proof, generated as a by-product of scanning.
- Insurers and customers price a trendA rating that is climbing is a different negotiation from a rating that is flat, in a renewal, a security questionnaire, or a cyber-insurance review.
A scanner can tell you today’s number the day it is installed. A timeline cannot be backfilled. It only exists if it has been recorded all along.
Illustrative trajectory on the 0–950 security rating, the same number your dashboard shows.
Brand Protection · Typosquatting Detection
Catch the typosquat before your customers do.
Attackers register a typosquat or look-alike of your domain, wrap it in a fresh TLS certificate, and weaponize it for phishing within hours. Telaris watches the certificate-transparency firehose and newly-registered-domain feeds in real time and surfaces impersonators before the first email is sent.
Real-time detection
CertStream (CT logs) + daily new-domain feeds, matched the moment a look-alike appears, not on a weekly crawl.
Scored & triaged
Every hit gets a transparent 0–100 risk score from match strength, live DNS/MX signals and lexical intent, so you work the real threats first.
Alerts that reach you
Email, Slack/Teams webhook and an in-app bell the instant a high-risk look-alike is detected. Immediate or daily digest.
Takedown, prepared for you
Abuse contacts looked up automatically (RDAP) and the report pre-drafted with screenshot evidence. You review and hit send. Nothing leaves in your name without your approval. Registrar, host and APWG desks are then submitted for you; Google Safe Browsing has no submission API, so you get a pre-filled form and one click. Afterwards it is watched continuously (DNS + HTTP): the case closes itself when the site goes dark, and re-opens with an alert if it returns.
Board-ready by default
Security your board can see, without logging in.
Most security tools make the practitioner faster and leave the CISO empty-handed at budget time. Telaris closes the loop: every stakeholder, CISO, CFO, auditor, board, gets the picture on schedule, in their inbox. No accounts to provision, no screenshots to paste into slides.
Monthly stakeholder report
On the 1st of each month, your distribution list receives the executive summary plus the full PDF report behind a secure link, valid 35 days, no Telaris account needed. The product reports your progress to the people who sign the budget.
Weekly delta digest
Leads with wins: "rating improved B → A−, 3 critical findings resolved, 2 attack paths eliminated." What changed this week, not a wall of unchanged state.
Trends beyond the score
Findings burn-down, attack-surface growth and ISO 27001 conformance drift, charted from daily posture snapshots. "Look how far we've come", with real lines, not anecdotes.
Alerts where you work
Critical CVEs, threat-intel matches and brand impersonators pushed to Slack, Teams or email within minutes of detection. One risk model, one alert stream, no console babysitting.
Also in the loop: peer benchmarking, your rating against comparable organizations, unlocking as the tenant pool grows. We never fabricate a percentile. During the trial, report recipients stay within your own company domain; paid plans distribute to any stakeholder.
4 criticals resolved · 2 attack paths eliminated · attack surface −6%
Secure link · valid 35 days · recipients need no Telaris account
See a real reportFramework coverage
Which duties land on you, and what we hand the auditor.
Telaris maps each obligation to the live cloud data that evidences it, control by control, and states what it did not assess.
Regulations that apply to you
EuropeAuto-detected from where you’re browsing, the frameworks legally mandated for organisations in the EU.
Transposition deadline Oct 2024 · national law varies
NIS2 Directive
160,000 EU entities · 18 critical sectors
Max fine
€10M / 2% essential · €7M / 1.4% important
Applies since Jan 2025
DORA
All EU financial entities, banks, insurers, fintechs
Max fine
1% of average daily turnover, per day
In force Aug 2024 · main obligations since Aug 2026 · high-risk to 2027
EU AI Act
By role and system: providers and deployers of in-scope AI
Max fine
€35M or 7% of global turnover
In force Dec 2024 · obligations from Dec 2027
Cyber Resilience Act
All products with digital elements sold in the EU
Max fine
€15M or 2.5% of global turnover
Operating in the GCC too? Switch the toggle, Telaris covers Qatar NCSA, UAE NESA, Saudi NCA (ECC) from the same live data. So do the voluntary attestations your customers ask for at renewal, ISO 27001 and SOC 2 Type II.
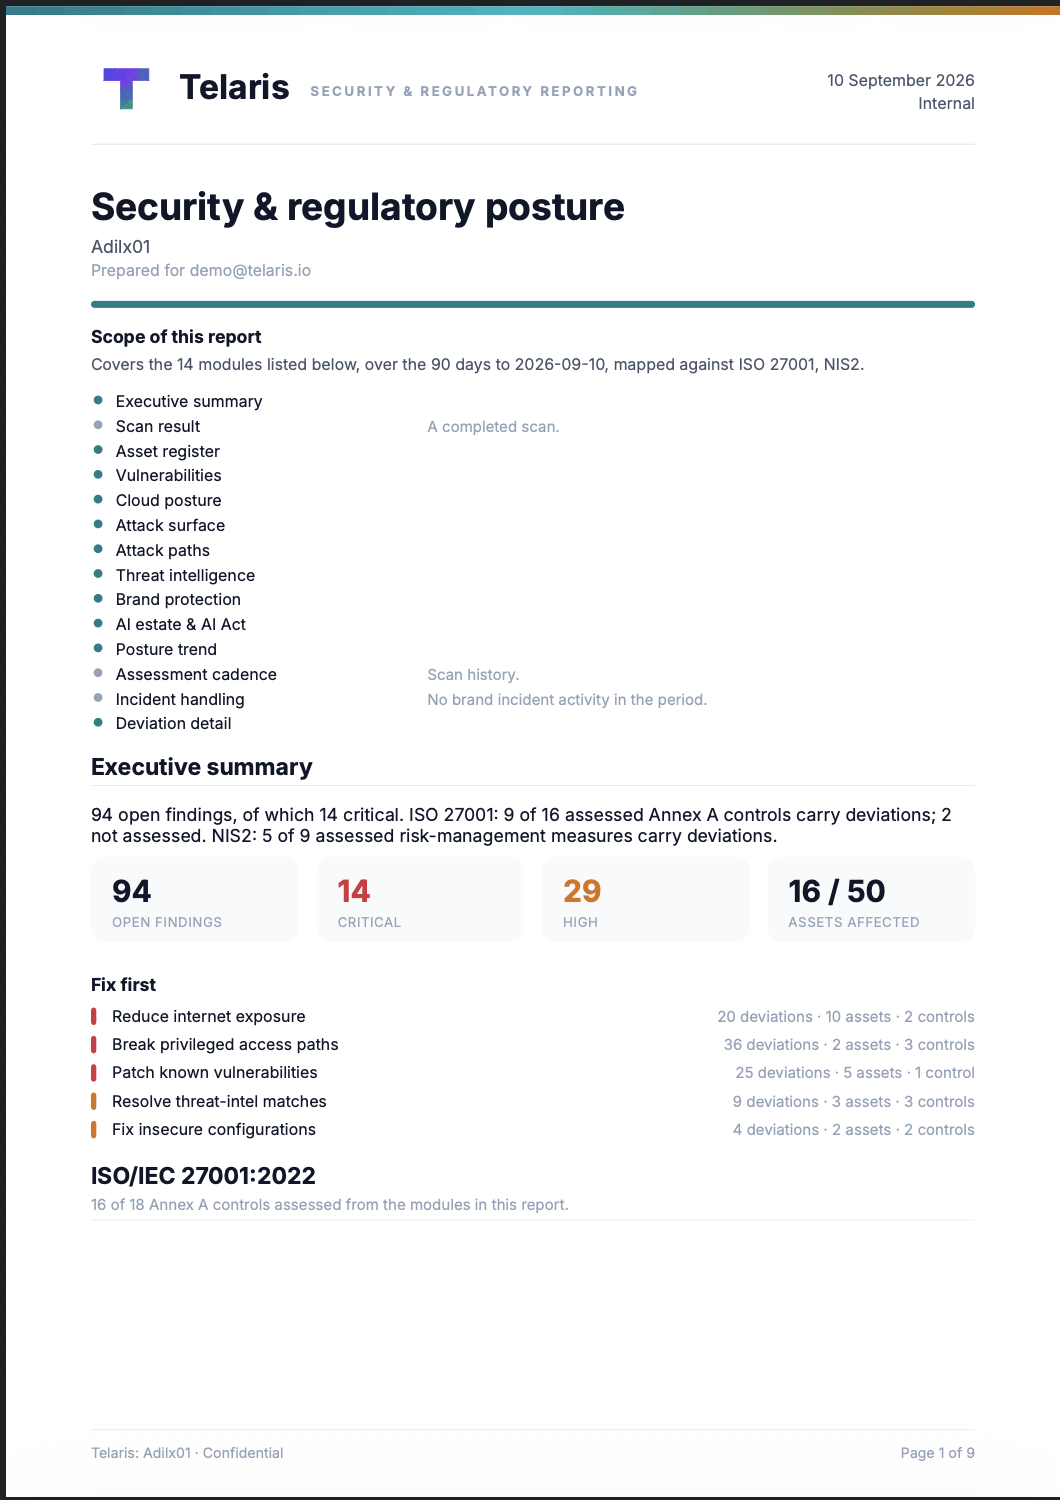
This is what comes out
A real first page, not a mock-up. Every module that produced nothing says why, the ISO section states how many controls it actually assessed, and nothing in it claims you are compliant, because Telaris reports record evidence and leave the verdict to your auditor.
How the evidence is producedPricing
Enterprise-grade security, mid-market price.
Annual plans in EUR, and a clear path to grow: included quotas stay lean, so you add cloud accounts, domains and AI capacity as you scale. Cancel anytime during your trial.
Starter
Get compliant and see your exposure.
- 2 cloud accounts · 5 users
- Asset discovery (AWS / Azure / GCP)
- Security exposure findings
- Brand Protection: 3 domains · 20 AI verdicts / mo
- AI Threat Chat: 100 queries / mo
- Email support
- EU AI Act: AI discovery (register & evidence pack in Professional)
Professional
The full platform for a lean security team.
- 8 cloud accounts · 15 users
- Everything in Starter
- Brand Protection: 10 domains · 80 AI verdicts / mo
- Attack paths & toxic combinations
- AI Threat Chat: 500 queries / mo
- EU AI Act: AI discovery, register & evidence pack
- IoC file scanner · API access
Enterprise
Scale, SLAs and audit-ready evidence.
- 20 cloud accounts · 40 users
- Everything in Professional
- Brand Protection: 30 domains · 300 AI verdicts / mo
- AI Threat Chat: 2,000 queries / mo
- Custom feeds · dedicated CSM · 4h SLA
Run the numbers your board will run. A single mid-market breach routinely runs into the millions, and NIS2 and DORA now carry fines of up to €10M or 2% of global turnover. Against that, Telaris Professional at €16,800 / year is the cheapest line item in your risk register.
Not ready to choose? Start free trial. No card, no commitment. Pick a plan later.
Trust & security
We never get write access to your cloud.
Agentless and read-only by design: a role you create, scoped to read, revocable by you in one click. Your data stays isolated, in-region, and yours.
Data isolation
Strict multi-tenant separation. Every customer’s data is logically isolated with tenant-scoped access controls and encryption in transit and at rest.
EU residency today · GCC on request
Your data lives on EU infrastructure in Germany. Evidence and telemetry stay in-jurisdiction. GCC-resident hosting is available on request for regulated buyers in the region; talk to us about your timeline.
Least-privilege access
Connect with agentless, read-only roles. Telaris never needs write access to your cloud, and never stores your workloads’ data.
30-day proof-of-value
See your real risk before you decide.
Scan in minutes
Agentless connection to AWS, Azure or GCP, scanning starts right after onboarding, nothing to deploy.
Report in one click
Generate a NIS2-ready compliance report from your live cloud data, instantly. Then put it on a monthly schedule to your stakeholders and never build a board deck again.
Fix what matters, and show it
Attack paths and exposures ranked by real exploitability, alerts in Slack or Teams, and trend lines that prove the burn-down to whoever signs the renewal.
“The tools that actually worked cost €150K–€500K a year and needed a 20-person team. The 80,000 companies covered by NIS2 had nothing designed for them, so I built it.”
Dr. Adil Bouti · Founder & CTO · 20 years in regulated-sector security
Frequently asked questions
- How fast can we show value?
- Connect your first cloud account and scanning starts within minutes, then generate a NIS2-ready compliance report in one click. No agents, no professional-services project.
- How is Telaris cheaper than enterprise security suites?
- One integrated platform instead of 5–7 separate tools, no large team to run it, and pricing that starts at €7,200/year, a fraction of what enterprise CSPM suites typically cost.
- Is it really agentless?
- Yes. Cloud asset discovery across AWS, Azure and GCP is fully agentless. Exposure and vulnerability scanning add depth without deploying anything inside your environment.
- Which regulations does it cover?
- NIS2, DORA and the Cyber Resilience Act in the EU, plus Qatar NCSA, UAE NESA and Saudi NCA (ECC) in the GCC. The same platform loads the framework for your region.
- Do I need a security team to run it?
- No. Telaris is built for lean teams, findings are prioritised by real exploitability, not raw CVSS, so you always know what to fix first. Critical findings reach you in Slack, Teams or email, so nobody has to babysit a console.
- How do I show progress to my board and auditors?
- Automatically. Telaris emails a monthly executive report to your stakeholder list, with the full PDF behind a secure link that needs no Telaris account, plus a weekly digest of what changed and trend charts for findings burn-down, attack surface and compliance drift. Your board sees measurable progress without ever logging in.
- Is my data isolated?
- Every customer’s data is logically isolated, enforced at the database layer with row-level security on the tenant key rather than left to application code to remember. Encrypted in transit and at rest, hosted in Germany.
- What access does Telaris need to my cloud?
- A read-only, agentless role. Nothing to install, and we never get write access to your accounts or your workloads. Telaris reads configuration and metadata to map your exposure; it never touches the data inside your systems.
- What happens after the 30-day proof-of-value?
- Nothing automatic. There is no card on file, so you are never charged by surprise. Keep the plan that fits (from €7,200/year), talk to us about annual terms, or walk away with the compliance evidence you already generated. No lock-in.
Find out what is actually in your cloud.
Connect one account and the first scan starts in minutes: your real attack surface, the paths that reach something that matters, and the evidence your next audit will ask for. Nothing to install, and we never get write access.
30 days free · no credit card · agentless, read-only. We never get write access to your cloud · cancel in one click